Direct breach exposes billions in vulnerabilities
The world’s largest cryptocurrency exchange has sustained its most severe security breach to date. On October 29, 2026, intruders exploited an internal office laptop to divert digital assets valued at approximately $6.3 billion. The unprecedented heist has sent shockwaves through the crypto sector and forced Binance to confront gaps in its operational safeguards.
How a single compromised device unlocked a financial juggernaut
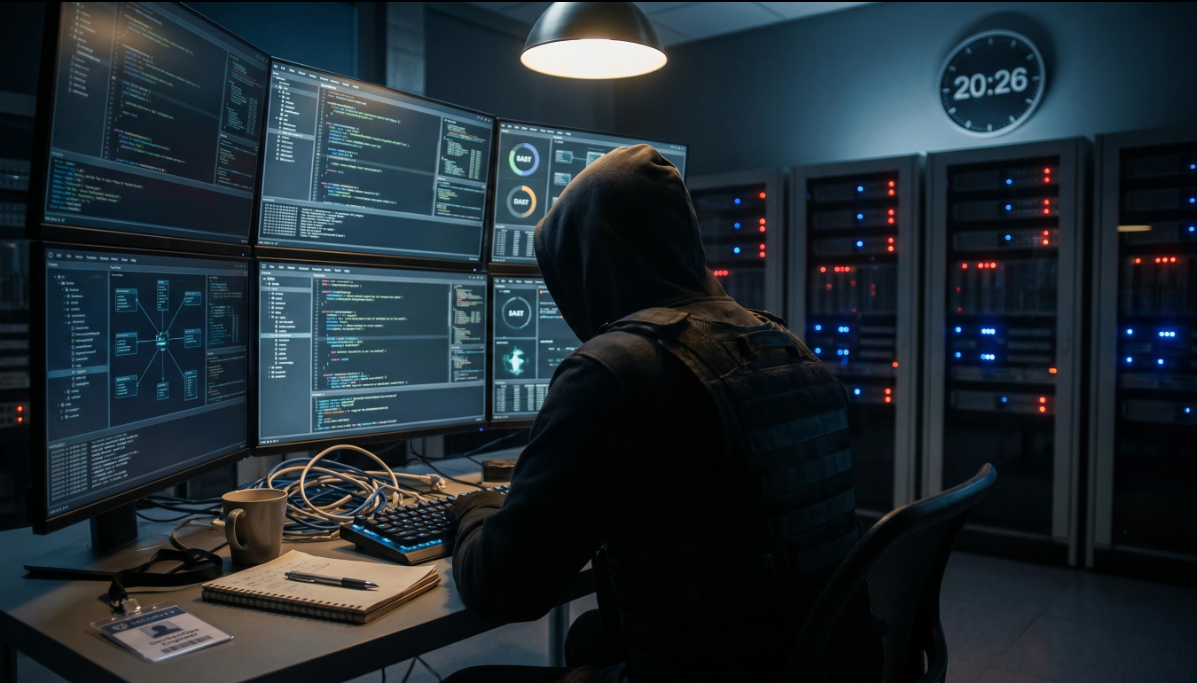
Investigations indicate that a DevOps engineer’s workstation was infiltrated, granting unauthorized access to internal systems. Once inside, attackers submitted fraudulent withdrawal requests without triggering core wallet security layers. Rather than cracking encryption or bypassing firewalls, they leveraged an existing human access point—underscoring that robust cyber defenses begin with hardened endpoints and strict privilege controls.
Critical questions over internal controls
This attack exposes potential deficiencies in multi-layer validation. If a compromised service account could authorize multi-billion-dollar transfers, segregation of duties and real-time monitoring clearly require reinforcement. Blockchain forensics suggests the illicit transactions were processed within 20 minutes, highlighting the need for instantaneous anomaly detection in high-value environments.
Partial recovery, persistent uncertainty
In response, Binance froze all deposits and withdrawals to secure operations. Partnering with stablecoin issuers, it claims to have frozen around $3 billion in diverted funds. The remaining $3.3 billion remains in circulation, leaving users and investigators searching for clues about its current whereabouts.
Possible link to state-backed actors
Preliminary assessments by blockchain analytics firms, including TRM Labs and Chainalysis, point toward TraderTraitor—a cybercrime syndicate tied to North Korea. Technical patterns and transaction trails support this hypothesis, though no official attribution has been made. The suspected involvement of a sophisticated state-linked group raises concerns about the scale and coordination of future threats.
Customer confidence hangs in the balance
Binance has pledged to cover all user losses using its Secure Asset Fund for Users (SAFU)—a $1 billion reserve—and corporate capital. While this commitment may temporarily calm markets, it does little to address the root concern: whether centralized platforms can reliably prevent internal breaches that bypass core security systems. The incident echoes previous failures, such as the $1.5 billion Bybit hack in early 2025, reinforcing a troubling pattern of large-scale crypto thefts.
What’s next for Binance and the crypto industry
Recovery efforts are underway, but the future hinges on transparency and reform. Independent security audits, detailed technical disclosures, and stricter validation protocols will be essential to restore trust. This attack may ultimately serve as a turning point—not only for Binance, but for an entire industry built on the promise of secure, decentralized value transfer.